Security was everywhere at KubeCon + CloudNativeCon Japan 2026 — but the AI-era version of the conversation has a new shape. The old question was “how do I isolate tenants?” The new one is “how do I isolate tenants and stay efficient when the workloads are hungry, expensive, and constantly shifting?” Three interviews cut straight to that tension.
The mandate: isolation and efficiency, at the same time
One speaker put the problem in the starkest terms. In the AI era you cannot compromise on security — but pushing isolation to its maximum makes efficiency collapse and cost explode. Their mandate targets exactly that conflict: maintain absolute isolation while simultaneously driving peak efficiency.
The failure mode they described is worth remembering: when you aggregate multiple workspaces into a shared environment, you get overlapping boundaries. Resource contagion sets in — a vulnerability in one workload can bleed into another. The fix is a hard, unambiguous boundary around each workload. Not “mostly separate,” not “separate enough.” A real wall.
That is the central design constraint of any multi-tenant AI platform, and it is harder than it looks because the thing that gives you isolation (dedicated everything) is the thing that destroys your utilization.
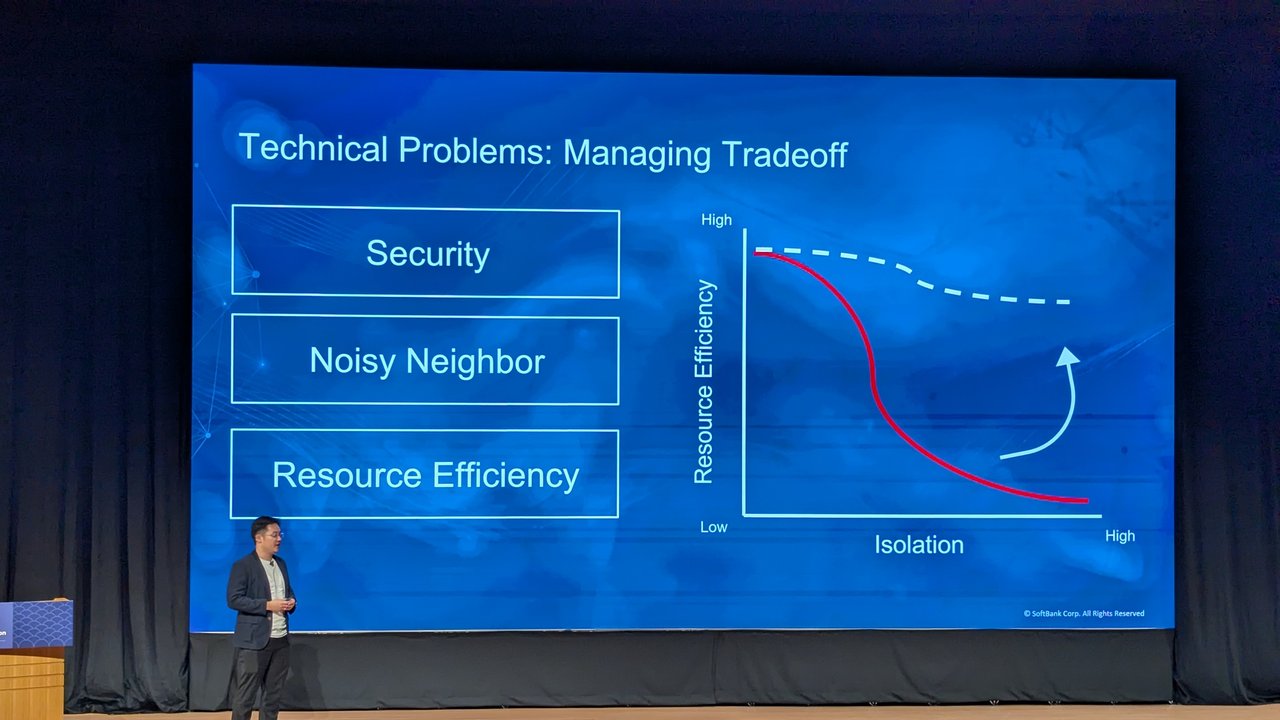
A slide from SoftBank’s keynote “Infinite Agents, Finite Kubernetes”: security, noisy neighbour and resource efficiency, with resource efficiency falling as isolation rises.
There is no single right answer — go hybrid
A second conversation landed on the pragmatic end of the same spectrum. As you push isolation up, overhead goes up. There is no single right answer — it depends entirely on your requirements.
Their approach at home is a hybrid: combine namespace isolation with dedicated tools. Namespaces give you lightweight multi-tenancy and flexibility; dedicated tools give you the hard boundaries the sensitive workloads need. The result is that you can balance cost and flexibility within a single cluster instead of standing up a fleet of single-tenant islands.
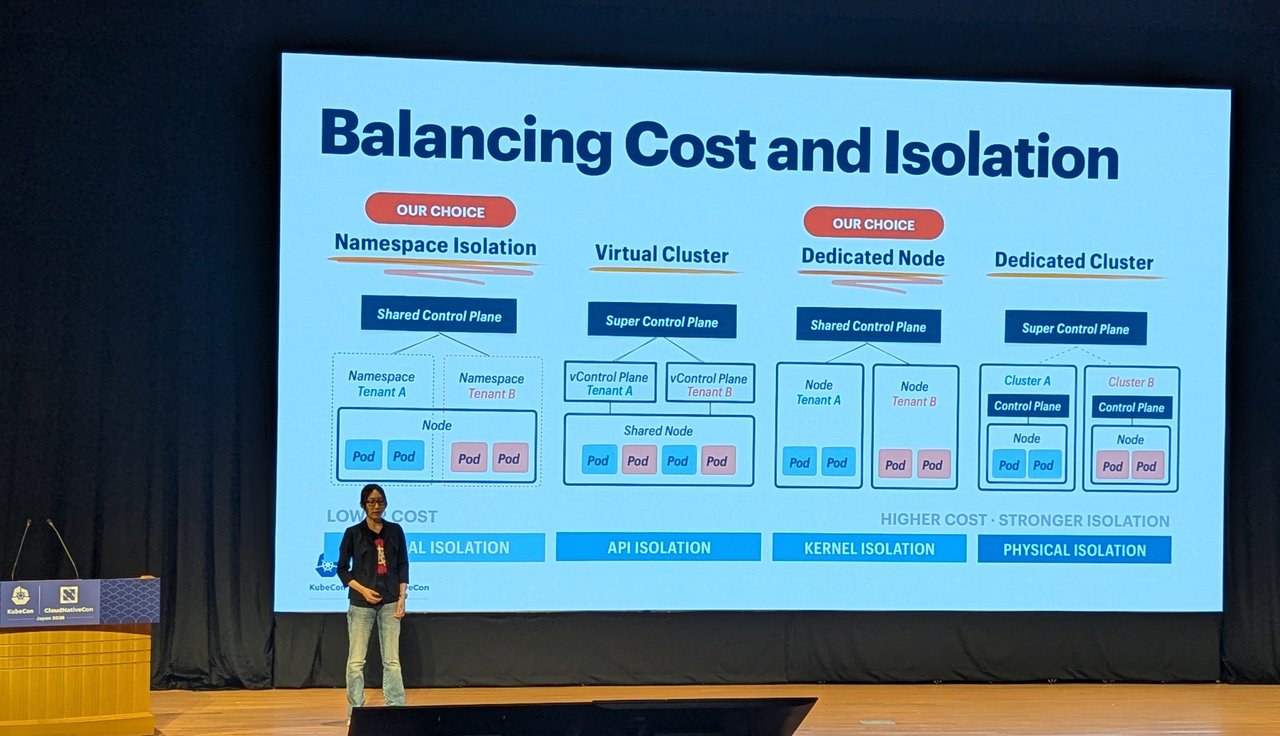
Preferred Networks’ keynote slide “Balancing Cost and Isolation”, with “Our Choice” marked above namespace isolation and dedicated nodes.
The honest caveat they added matters: when you choose the more shared approach, you take on more responsibility yourself. Because tenants are less isolated, you have to build the rest of the safety — policy, quotas, network controls — yourself. Hybrid is not “free isolation.” It is “isolation you earn through engineering.”
Sovereignty: a trusted orchestration layer on open source
The third thread was strategic rather than tactical. A representative described a sovereign orchestration layer — a trusted foundation built on open-source technologies, aimed at giving customers technology they can rely on. The framing was “sovereign” in the sense of control and trust: infrastructure you can stand behind, not rent blindly from a black box.
For enterprises and public-sector teams, that is the layer AI actually forces you to think about. A model is only as trustworthy as the orchestration underneath it. Building that layer on open source means the trust is auditable, portable, and not hostage to a single vendor’s roadmap.
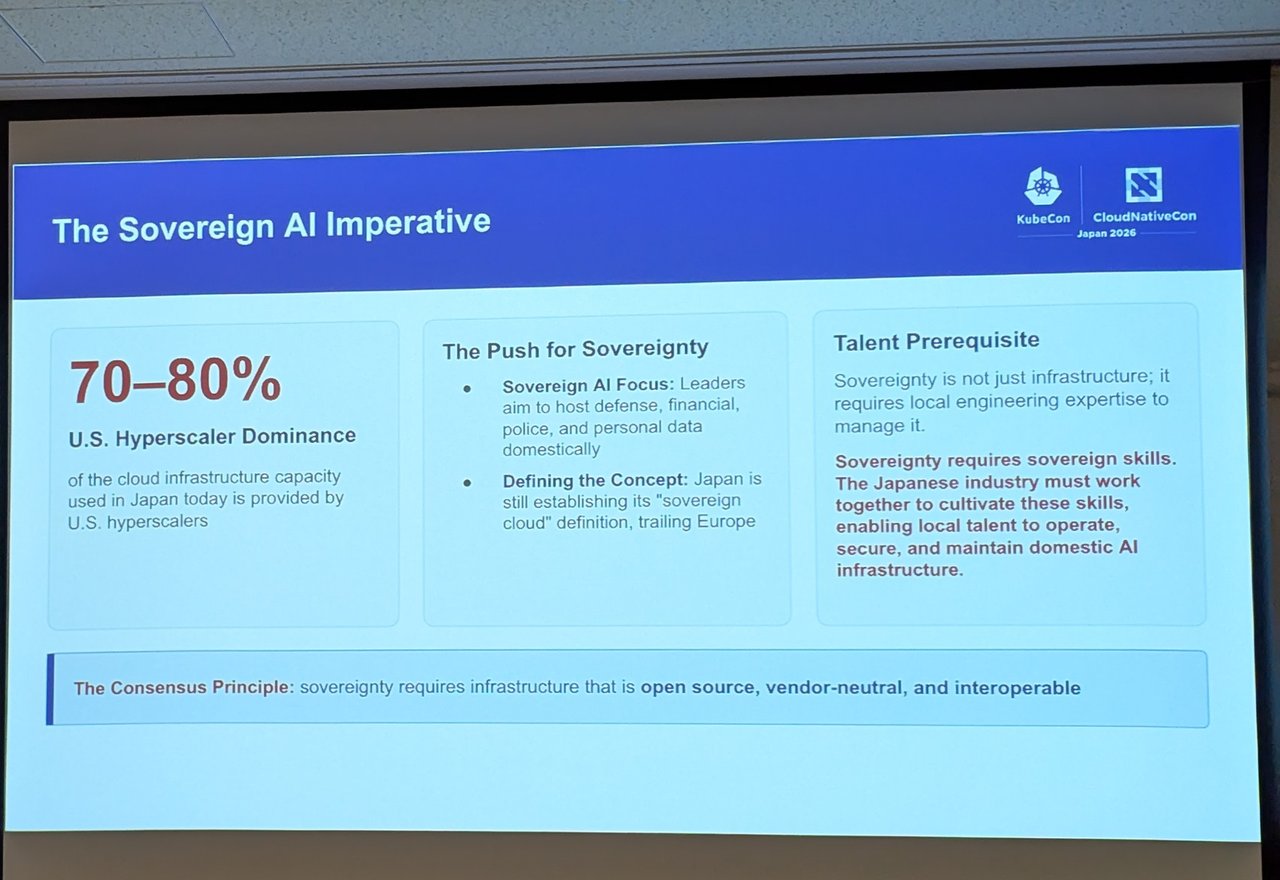
From the CNCF press briefing: “The Sovereign AI Imperative”. The principle on the slide: sovereignty requires infrastructure that is open source, vendor-neutral and interoperable.
Three takeaways for platform engineers
- Draw the boundary before you draw the architecture. Decide your isolation model first; it determines your cost ceiling.
- Hybrid is the mature default. Pure shared is too risky for AI; pure dedicated is too expensive. Mix namespace isolation with dedicated tools and own the gap.
- Sovereignty is a platform feature. An open-source, trusted orchestration layer is how you keep control as AI moves into regulated and high-stakes workloads.
None of this is theoretical — it is the day-to-day reality of running AI in production, and it was the quiet backbone of a lot of hallway-track conversations in Yokohama.
See the rest of my Japan 2026 coverage in the KubeCon Japan 2026 media-partner preview.